Crypto: Binance Hack Began With a Fake Job Interview
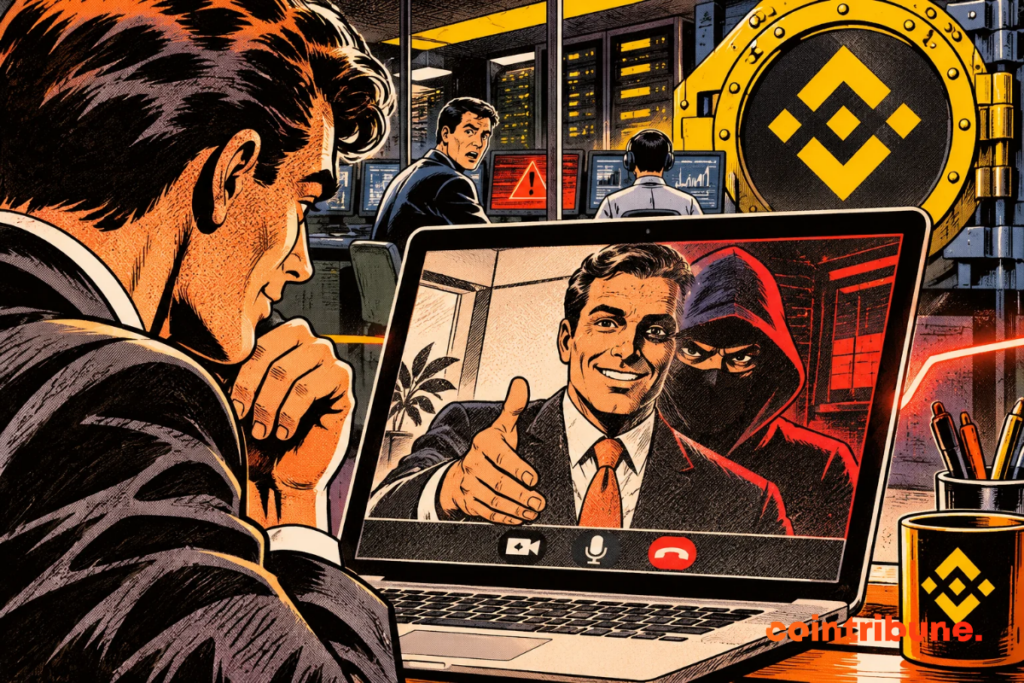
A fake job interview helped hackers infect a Binance engineer’s work computer before the $6.34 billion crypto theft on October 29, 2026. In a report released on November 3, the exchange described a months-long infiltration involving malicious software, stolen credentials and the misuse of an internal AI tool. The attackers ultimately reached the infrastructure responsible for authorizing transactions from Binance’s cryptocurrency wallets.
In Brief
- Hackers tricked a Binance engineer into downloading an infected coding assignment after two fake interviews.
- The attackers later used an internal AI tool and stolen deployment credentials to access wallet systems.
- Binance says it has replenished 98% of affected assets and frozen or intercepted $2.85 billion.
A Fake Recruitment Process Helped Hackers Enter Binance
The investigation reveals a much longer operation than initially suspected. Following the Binance hack linked to North Korean attackers, the exchange traced the first signs of compromise back to June 2026, four months before the theft.
At that time, a wallet operations engineer downloaded a modified Homebrew installation while searching for an AI-powered coding tool. Homebrew is commonly used by developers to install software on macOS and Linux.
Binance detected the suspicious installation, replaced the employee’s computer and reset the affected credentials. However, the attackers had already gathered information about the engineer’s responsibilities and colleagues.
A second operation followed in September.
Another Binance engineer was approached through a legitimate recruitment platform by someone posing as a project director. The supposed employer offered a software development position.
The candidate completed a video interview with a fake human resources representative, who shared social media profiles and personal photographs to appear credible. A second interview followed with someone pretending to be the company’s CEO.
At the end of the process, the engineer received a programming assignment. The exercise required downloading a code repository onto his work computer. Hidden inside was malicious software designed to execute during the setup process.
According to Binance, the malware escaped the device’s security protections. The attackers now had an entry point into another employee’s computer. They had spent months preparing the operation without directly attacking a blockchain.
Hackers Used an Internal AI Tool to Reach Crypto Wallets
The next phase began on October 20. Using the computer compromised during the fraudulent recruitment process, the attackers exploited an internal AI tool to reach two engineers involved in Binance’s wallet infrastructure.
They discovered a deployment token on one of the compromised devices. This credential allowed them to deploy software containers within the company’s infrastructure.
That access became crucial nine days later.
The incident should not be described as an autonomous AI attack. Binance says the hackers misused an existing internal tool as part of an intrusion directed by human operators.
The role of AI is attracting attention as the industry faces other cybersecurity threats. Cointribune recently reported a separate AI-assisted intrusion affecting Chainalysis, although the company said that incident was unrelated to the Binance theft.
On October 29, between 17:15 and 19:56 UTC, the Binance attackers accessed a third engineer’s computer. They used stolen permissions to deploy a container and execute a malicious script connected to wallet transaction signing.
Unauthorized transfers began at 20:05 UTC.
Within four minutes, five wallets transferred 233.46 million XRP to an attacker-controlled address. Other transactions involved 970,500 SOL, 18,270 BTC and approximately 44.2 million OP tokens.
Ethereum presented an additional technical challenge.
The attackers used EIP-7702, a mechanism introduced in 2025 that allows certain wallet operations to be delegated to smart contracts.
Malicious authorizations enabled transactions outside Binance’s normal withdrawal procedures. The exchange says it completed the revocation of the affected delegation at 00:10 UTC on October 30.
By then, billions of dollars had already left its wallets.
Binance Replenishes Assets and Strengthens Security
Binance estimates the incident affected approximately $6.34 billion in digital assets. According to its November 3 report, around $2.85 billion had been frozen or intercepted. The exchange also reported replenishing 98% of the affected assets using company resources.
These are two different measures. The 98% figure does not mean that hackers returned nearly all the stolen cryptocurrency. It refers to the assets Binance replaced from its own reserves and other financial resources.
The company says customers will not bear the financial losses. Binance has replaced compromised computers, revoked affected credentials and rebuilt its transaction-signing environment. Its internal AI tools have also been reinstalled with tighter access controls.
An independent cybersecurity review is planned. The exchange also claims to have detected and prevented 57 suspected North Korea-linked cyberattack attempts during 2026.
The FBI has attributed the October 29 theft to TraderTraitor, a group associated with North Korea. Pyongyang rejects the accusation.
The recovery of stolen assets remains a separate challenge from rebuilding Binance’s security systems.
For users, the restoration of withdrawal services and the exchange’s financial position will remain important indicators. Binance has already recorded $2.3 billion in daily net inflows after the hack, although those deposits do not erase the previous withdrawals. The company’s next security disclosures will help establish whether the weaknesses exploited during this operation have been fully addressed.
Maximize your Cointribune experience with our "Read to Earn" program! For every article you read, earn points and access exclusive rewards. Sign up now and start earning benefits.
Enseignante et ingénieure IT, Lydie découvre le Bitcoin en 2022 et plonge dans l’univers des cryptomonnaies. Elle vulgarise des sujets complexes, décrypte les enjeux du Web3 et défend une vision d’un futur numérique ouvert, inclusif et décentralisé.
The views, thoughts, and opinions expressed in this article belong solely to the author, and should not be taken as investment advice. Do your own research before taking any investment decisions.