Crypto Hack: DOJ Seeks to Seize $1.2B Stolen from Binance
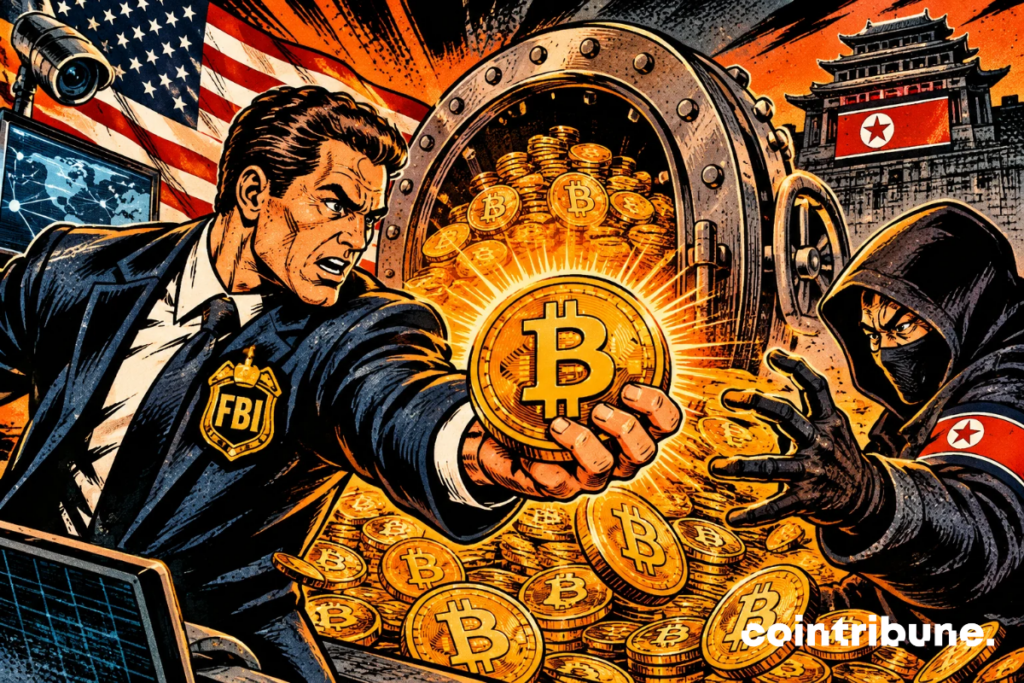
On November 12, 2026, the United States Department of Justice (DOJ) announced two operations against North Korean networks involved in cryptocurrency theft. Authorities obtained a court order to seize or freeze more than $1.2 billion from the Binance hack. They also neutralized the cloud infrastructure of FaceStealer, a deepfake manipulation campaign responsible for over $400 million in crypto theft over 18 months. These two cases illustrate different methods but the same strategy of exploiting the crypto ecosystem.
In brief
- The DOJ obtains a court order targeting more than $1.2 billion stolen during the Binance hack.
- U.S. authorities and partners have already frozen over $2.7 billion of stolen crypto funds.
- The FBI attributes the Binance hack to the North Korean group TraderTraitor.
- The FaceStealer network allegedly stole over $400 million in cryptocurrencies in 18 months using social engineering and deepfake techniques.
- The FBI seized more than 900 webcam videos related to this campaign.
More than $1.2 billion targeted after the Binance hack
The DOJ obtained court authorization to seize or freeze more than $1.2 billion from the Binance hack that occurred on October 29, 2026. This amount represents part of the digital assets already frozen thanks to cooperation between U.S. authorities and crypto sector actors.
According to the official Department of Justice statement, more than $2.7 billion has been frozen from loot estimated at more than $6 billion. The FBI attributes this attack to members of the North Korean army known as TraderTraitor.
Investigators continue to trace the crypto funds. Those behind the Binance hack are trying notably to launder the assets through:
- bridges;
- mixing services;
- various cryptocurrency exchange platforms.
They even managed to launder $430,000 using memecoins created on the NEAR protocol.
Important clarification: the court order covering $1.2 billion does not mean this sum has been definitively recovered. Freezing assets, seizing them, and possible confiscation are separate steps.
Binance states it has mobilized more than $6.34 billion in resources to cover the affected assets. In its announcement of November 12, the crypto exchange also indicated having published a new snapshot of its reserves. This financial coverage announced by the company should not be confused with the judicial recovery of stolen funds.
FaceStealer: $400 million stolen through deepfakes
The second U.S. operation targets the cloud infrastructure used by FaceStealer. According to the DOJ, this North Korean campaign caused more than $400 million in crypto thefts over the last 18 months.
Its operation relies on social engineering:
- Hackers first use compromised accounts to invite their victims to videoconferences.
- They then discreetly record their webcam and broadcast prerecorded videos or deepfakes of people known to their interlocutors.
Once trust is established, hackers simulate a technical problem. They then offer a link or manipulation supposed to restore the meeting’s function. In reality, this purported solution installs malware on the victim’s computer.
Hackers can then steal crypto assets, hijack communication accounts, or exploit compromised computer access. Some intrusions reportedly manifested months after the initial infection.
The campaign also targets open-source software developers and maintainers. The potential goal: to access their devices and code repository accounts to prepare attacks against the software supply chain.
In this operation, the FBI seized over 900 webcam videos under a federal warrant. The agency also launched a dedicated FaceStealer space. It gathers information on the threat as well as recommendations for potentially compromised individuals.
This method is part of a larger context of infiltration of the crypto ecosystem by North Korean actors. Reference is made notably to alerts regarding fake North Korean developers targeting companies in the sector.
Two American operations against different theft methods
The Binance and FaceStealer cases do not denote a single hack:
- The first concerns the massive diversion of assets from an exchange platform, attributed by the FBI to TraderTraitor.
- The second relies on manipulating victims through fake videoconferences, recorded videos, and deepfakes.
However, their comparison reveals the extent of threats targeting the crypto sector. Cybercriminals no longer only try to compromise wallets or platforms. They also exploit professional relationships, communication tools, and development environments to obtain sensitive access.
The DOJ now continues tracing, seizing, and confiscating assets from the Binance hack. For crypto actors, the case highlights the importance of communication and development environment security, beyond just digital wallet protection.
Maximize your Cointribune experience with our "Read to Earn" program! For every article you read, earn points and access exclusive rewards. Sign up now and start earning benefits.
My name is Ariela, and I am 31 years old. I have been working in the field of web writing for 7 years now. I only discovered trading and cryptocurrency a few years ago, but it is a universe that greatly interests me. The topics covered on the platform allow me to learn more. A singer in my spare time, I also cultivate a great passion for music and reading (and animals!)
The views, thoughts, and opinions expressed in this article belong solely to the author, and should not be taken as investment advice. Do your own research before taking any investment decisions.