Crypto: Ledger Investigates Tampered Wallets After $93 Million in Losses
The Ledger case takes a new turn. The crypto wallet manufacturer confirms having discovered an unauthorized hardware implant in the device of a user affected by recent thefts in Southeast Asia. The theory of physical tampering before delivery is gaining strength. The suspected losses now approach 93 million dollars, but this amount has not been validated by Ledger.
In brief
- Ledger confirms a hardware implant in the device of at least one affected user.
- Crypto losses are estimated up to 93.4 million dollars by independent analysts.
- The reseller CryptoBilis has suspended its hardware wallet sales during the investigation.
Ledger finally confirms physical tampering
A few days earlier, Ledger was still investigating without confirming the cause. Over 86 million dollars in losses were then associated with wallets purchased from CryptoBilis, a reseller operating in Southeast Asia. On Saturday, October 10, the company provided a much more concrete element.
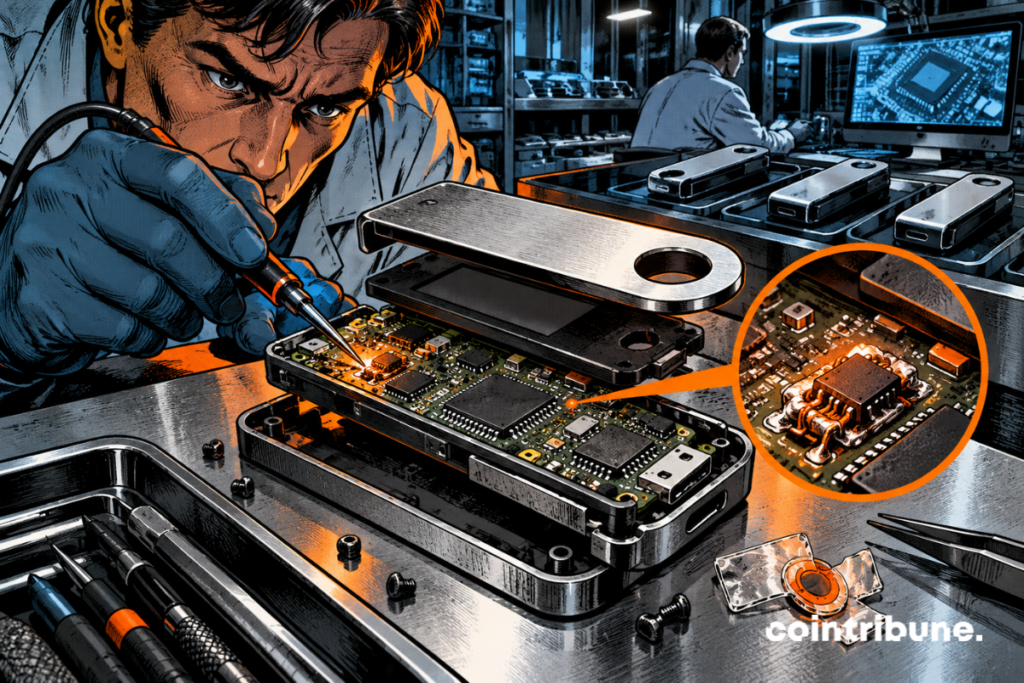
A device belonging to one of the affected users contained an unauthorized hardware implant. This discovery seriously strengthens the hypothesis of a supply chain attack.
CryptoBilis notably sold Ledger devices in Indonesia, Malaysia, and the Philippines. Ledger had already asked it to temporarily stop sales and shipments during the investigation. The reseller has since suspended the sale of all its hardware wallets.
Ledger nonetheless emphasizes one point: there is currently no evidence that its infrastructure, systems, or internal services have been compromised. This distinction is important. The problem could be located after manufacturing, somewhere between the manufacturer and the end user.
An implant capable of spying on the recovery phrase
The former Mt. Gox boss, Mark Karpelès, had published images of a modified Ledger Nano X even before Ledger’s official confirmation. Inside, he claims to have found a small circuit board hidden behind the screen. The device notably included cellular communication components.
Its presumed operation is particularly worrying for crypto security. The implant would not need to break Ledger’s Secure Element. It could simply monitor the information sent to the screen during wallet setup.
It is precisely at this moment that the 24 recovery words appear. Once this phrase is intercepted, the attacker can theoretically recreate the wallet on another device and move the assets without needing the original Ledger.
The device could even leave the original secure chip intact. A device modified in this way would therefore be likely to appear authentic during some checks. The case illustrates another aspect of supply chain attacks. In 2025 already, Ledger’s CTO warned of an NPM package compromise threatening crypto users. This time, the problem is not hidden in software. It is directly in the hardware.
Up to $93 million in crypto under watch
The figures keep evolving. Yfarmx estimates the suspected losses at about 93.4 million dollars spread across 471 addresses. Bitquery reaches about 92.9 million across 311 unique addresses.
Ledger has not confirmed any of these totals. It is also not established that every counted address corresponds to a physically modified device. For now, Ledger has publicly confirmed the implant on only one device belonging to a concerned user.
Bitcoin, ether, and several stablecoins are among the assets tracked in the suspicious transactions. Ledger recommends people who recently bought a device from CryptoBilis not to start its setup. For those who have already used it, the company advises considering a transfer to a new signer with a new recovery phrase.
Reusing the same 24 words on a new device would obviously solve nothing if the phrase has already been intercepted. Ledger is also working on new protections against physical tampering. The incident occurs while hardware wallets are precisely marketed as a solution to keep crypto keys away from centralized platforms. Yet, no system protects against all scenarios.
A fake Ledger app had already enabled the diversion of nearly 9.5 million dollars in crypto earlier this year. Here, the attack is different. The user can follow the usual rules, keep their recovery phrase offline, and not sign any suspicious transaction. If the device itself was modified before arrival, the threat starts even earlier. This is precisely what Ledger must now determine: how many devices have been tampered with, when, and by whom.
Maximize your Cointribune experience with our "Read to Earn" program! For every article you read, earn points and access exclusive rewards. Sign up now and start earning benefits.
Fascinated by Bitcoin since 2017, Evariste has continuously researched the subject. While his initial interest was in trading, he now actively seeks to understand all advances centered on cryptocurrencies. As an editor, he strives to consistently deliver high-quality work that reflects the state of the sector as a whole.
The views, thoughts, and opinions expressed in this article belong solely to the author, and should not be taken as investment advice. Do your own research before taking any investment decisions.